Beyond the Drawer: Storing Payment Receipts Securely – Best Practices for Business Compliance

The Criticality of Secure Receipt Management

In the age of digital transactions, businesses generate vast quantities of payment receipts containing sensitive information—from transaction identifiers and items purchased to truncated card numbers and customer names. Improper handling of this data is a leading cause of data breaches, resulting in severe financial penalties, regulatory non-compliance, and devastating reputational damage. Adopting robust protocols for secure payment receipt storage is not optional; it is a foundational requirement for modern business operations.

Navigating Regulatory Requirements and Risks

The regulatory landscape mandates meticulous attention to data protection. Compliance standards such as the Payment Card Industry Data Security Standard (PCI DSS) dictate strict guidelines for handling cardholder data, even if only partial data (like truncated card numbers) is present on receipts. Additionally, global privacy laws like the GDPR and regional acts like the CCPA impose obligations concerning the storage and processing of any personally identifiable information (PII) linked to transactions. Failure to adhere to these rules can trigger costly audits and fines that far outweigh the cost of implementing a secure system.

Digital Storage: The Path to Modern Security

The first critical step toward enhanced security is minimizing reliance on physical, paper-based receipts, which are inherently vulnerable to physical theft and environmental damage. Transitioning to digital storage provides scalability and advanced protection features. When choosing a system, ensure that the cloud or local servers utilized employ end-to-end encryption for data both in transit and at rest. Look for providers who maintain recognized security certifications, such as ISO 27001, verifying their commitment to information security management.

Implementing Zero-Trust Access and Encryption

The cornerstone of secure payment receipt storage is the principle of least privilege (PoLP) and stringent access control. Only authorized personnel, those who absolutely require access for auditing, compliance checks, or chargeback defense, should be able to view receipt data. Implement mandatory multi-factor authentication (MFA) for all systems housing sensitive records. Crucially, all archived digital receipt data must be protected using strong cryptographic methods, typically AES-256 encryption. This ensures that even if a data store is compromised, the information remains unreadable and useless to unauthorized actors.

Defining Clear Retention and Destruction Policies

Storing data longer than legally required exponentially increases the associated risk. Businesses must establish and strictly adhere to clear, documented data retention schedules, which often range from three to seven years depending on local financial and tax laws. Once the retention period expires, data must be permanently and irrecoverably destroyed. For digital files, this means using secure cryptographic erasure or certified secure deletion techniques. Physical receipts must be handled by certified shredding services using cross-shredding methods. Regularly auditing these destruction protocols is vital to maintain compliance and minimize liability.
Tagged : / / / / / /

Storing Payment Receipts Securely: Essential Best Practices for Business Compliance and Data Protection

The Critical Importance of Secure Payment Receipt Storage

In today’s digital economy, businesses process thousands of transactions annually, each generating a crucial piece of data: the payment receipt. While often overlooked, the secure storage of these receipts is not merely a bureaucratic task; it is a fundamental pillar of data protection, regulatory compliance, and risk mitigation. Mismanaged receipts, whether digital or physical, pose serious risks, including exposure to tax penalties, audit failures, and crippling data breaches that violate standards like PCI DSS (Payment Card Industry Data Security Standard).

Establishing Clear Legal and Retention Policies

Before implementing any storage solution, businesses must first understand their legal obligations. Retention periods for financial documents vary widely depending on jurisdiction and the nature of the transaction, typically ranging from three to seven years. A cornerstone of secure payment receipt storage is establishing a transparent, documented retention schedule that mandates when records must be kept and, equally important, when they must be destroyed. Consulting with legal and financial advisors ensures compliance and streamlines future audits.

Best Practices for Digital Receipt Management

For most modern businesses, digital storage offers superior security, scalability, and accessibility compared to traditional paper filing. However, digital storage must be managed correctly. Businesses should utilize dedicated Document Management Systems (DMS) or secure, cloud-based archiving solutions. Never rely on local hard drives or generic, unencrypted cloud storage. Crucial digital security measures include:

  • Encryption: All archived receipts must be protected using strong, industry-standard encryption protocols (e.g., AES-256) both in transit and at rest.
  • Access Control: Implement the principle of least privilege. Only authorized personnel should have access, requiring multi-factor authentication (MFA) for entry into the storage system.
  • Regular Backups: Ensure redundant, encrypted backups are performed frequently, stored offsite, and regularly tested for restoration integrity.

Securing Physical Receipt Archives

While digital storage is preferred, some businesses still rely on physical records. Secure storage for paper receipts demands strict procedural controls. Receipts should be stored in locked, fireproof cabinets located in restricted-access areas. Maintain comprehensive audit logs tracking who accesses the physical archives and why. The primary risk with physical receipts is unauthorized access or environmental damage; proper physical security is non-negotiable.

The Final Step: Secure Destruction Protocols

Once the mandatory retention period expires, the secure destruction of receipts is mandatory. Failing to destroy expired records increases liability. For digital files, this requires cryptographic erasure or physical destruction of the storage media to ensure the data is irrecoverable. For physical documents, cross-shredding is the minimum standard, ensuring the pieces cannot be reassembled. Implementing and regularly auditing these destruction protocols closes the security loop, protecting customer data and demonstrating ongoing due diligence.

Tagged : / / / / / /

The Future of Finance: 4 Digital Documentation Trends Every Business Must Adopt

Why Digital Documentation is No Longer Optional

In the rapidly evolving landscape of global commerce, traditional paper-based systems are a liability. Businesses are now aggressively adopting digital solutions to manage financial records, driven by demands for efficiency, security, and instantaneous accessibility. Staying competitive requires understanding the cutting-edge practices in Digital Finance Documentation. Ignoring these shifts means falling behind in compliance, speed, and data integrity.

Trend 1: AI and Hyper-Automation for Document Processing

One of the most transformative trends is the integration of Artificial Intelligence (AI) into documentation workflows. AI-powered tools can now automatically ingest invoices, contracts, and expense reports, extracting critical data points with near-perfect accuracy. Hyper-automation, which combines AI with Robotic Process Automation (RPA), is drastically reducing the manual effort required for data entry, reconciliation, and audit preparation. This not only speeds up month-end closes but significantly minimizes human error, ensuring that financial records are timely and precise.

Trend 2: Blockchain for Immutable Record Keeping

Security and verification are paramount in finance. Blockchain technology is emerging as a critical tool for creating an immutable, transparent ledger for financial documents. By timestamping and encrypting records on a distributed ledger, businesses can guarantee the authenticity and integrity of critical documents like loan agreements, supply chain invoices, and regulatory filings. This eliminates disputes over record versions and dramatically simplifies the audit trail. While full adoption is nascent, industry leaders are already piloting blockchain applications to secure their core Digital Finance Documentation.

Trend 3: Cloud-Native Solutions and Unified Data Access

The days of siloed servers are over. Modern financial management relies heavily on cloud-native solutions that provide scalable storage and unified data access across global operations. Moving documentation to specialized financial data clouds ensures high availability and robust disaster recovery. Furthermore, advanced platforms are leveraging API connectivity to integrate documentation systems directly with Enterprise Resource Planning (ERP) and Customer Relationship Management (CRM) tools, creating a seamless, end-to-end operational flow.

Trend 4: Enhanced Regulatory Technology (RegTech) and Compliance

The complexity of global financial regulations (like GDPR, CCPA, and evolving tax standards) requires proactive documentation strategies. RegTech solutions embedded within documentation platforms automatically monitor changes in regulatory requirements and flag documents that need updates or specific retention periods. For businesses managing sensitive client data, this automated compliance feature is crucial for avoiding costly fines and maintaining operational licenses. Investing in compliant Digital Finance Documentation tools is now a strategic necessity, not just a back-office requirement.

Future-Proofing Your Financial Operations

The shift toward entirely digital financial systems is irreversible. Businesses that embrace these trends—leveraging AI for speed, blockchain for trust, and cloud technology for accessibility—will gain a significant competitive edge. Updating your documentation infrastructure should be a key priority in your organization’s digital transformation roadmap to ensure security, compliance, and long-term viability.

Tagged : / / / / / / /

Securely Storing Payment Receipts: Essential Best Practices for Business Compliance

The Criticality of Secure Receipt Storage

In the modern business landscape, payment receipts are more than just proof of purchase—they are sensitive documents containing valuable financial data. For businesses, securely storing payment receipts is not merely an administrative task; it’s a foundational requirement for legal compliance, fraud prevention, and maintaining customer trust. Failing to implement robust storage practices exposes your organization to severe risks, including data breaches, hefty regulatory fines, and potential reputational damage.

Why Secure Storage is Non-Negotiable

The primary drivers behind implementing stringent receipt storage protocols are regulatory compliance and data protection. Depending on your industry and location, various regulations mandate how long and how securely you must retain transactional data. For example, tax authorities (like the IRS) require retention for several years. More critically, standards like the Payment Card Industry Data Security Standard (PCI DSS) dictate how cardholder data, which often appears on detailed receipts, must be handled and protected. Secure storage acts as your primary defense against internal theft and external cyberattacks targeting sensitive customer financial information.

Digital Transformation: The Shift to Electronic Storage

While physical paper receipts pose storage challenges (vulnerability to fire, water damage, and disorganized archiving), modern best practices overwhelmingly favor electronic storage. Digital records, when managed correctly, offer superior security, accessibility, and longevity. Businesses should transition to a centralized, cloud-based system that meets industry security standards. However, digitization is only effective if security measures are fully integrated.

Essential Best Practices for Digital Receipt Management

1. Implement Strong Encryption

Any system used to store receipt images or data must utilize robust encryption, both in transit (when data is uploaded or retrieved) and at rest (when data is sitting on a server). Use industry-standard AES-256 encryption or higher to render the data unreadable to unauthorized parties.

2. Restrict and Control Access

Access to stored receipts should operate on the principle of least privilege. Only employees who absolutely require access for auditing or administrative tasks should have permission. Implement multi-factor authentication (MFA) for all system logins and maintain detailed audit logs documenting every access and modification.

3. Regular, Secure Backups

Data loss is a major risk. Establish a schedule for frequent, automated backups of all receipt archives. These backups should also be encrypted and stored separately, preferably in geographically diverse locations, to ensure business continuity in case of a localized disaster or system failure.

4. Redact Sensitive Information

Minimize risk by minimizing the data you store. Ensure that your point-of-sale (POS) systems and archiving processes automatically redact sensitive information, such as the full Primary Account Number (PAN) or the card verification value (CVV), from the receipt copy before it is permanently stored. The fewer full card numbers you retain, the lower your risk exposure.

Adhering to Retention and Disposal Policies

Knowing when to securely dispose of receipts is just as important as knowing how to store them. Establish clear data retention policies based on legal and regulatory requirements (typically 3 to 7 years, but this varies). Once the mandatory retention period expires, the records must be disposed of securely. For digital records, this means permanent, irrecoverable deletion, often requiring specialized data sanitization techniques to comply with privacy laws.

Conclusion

Securely storing payment receipts is a continuous commitment, not a one-time setup. By moving to encrypted digital archives, tightly controlling access, and strictly adhering to data retention schedules, businesses can transform a liability into a secure, auditable asset, protecting both their financial health and the privacy of their customers.

Tagged : / / / / / /

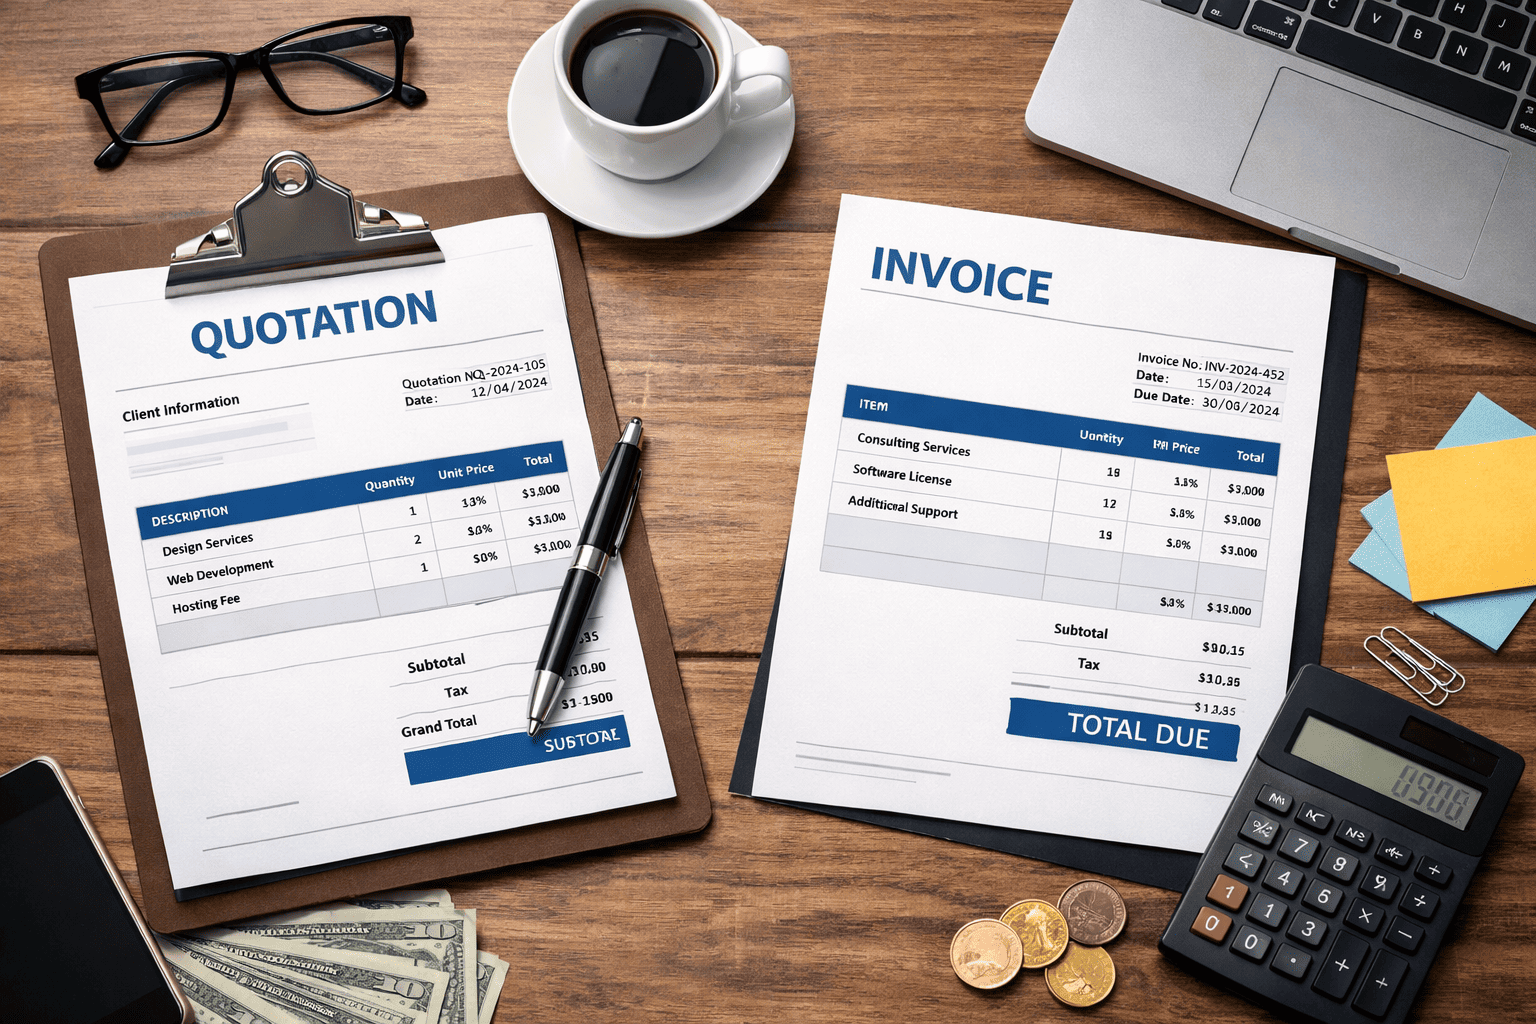
The Critical Importance of Industry Specific Quotation Formats for Business Success

In the competitive landscape of modern business, a simple quote is often the dividing line between winning a lucrative contract and losing it. Yet, simply listing prices is not enough. The structure, terminology, and legal requirements of a quotation must meticulously align with the industry in which you operate. This adherence to Industry Specific Quotation Formats is not merely bureaucratic overhead; it is a fundamental pillar of professionalism, compliance, and profitability.

Why Standardized Quotes Are Non-Negotiable

Standardization ensures clarity. When a prospective client receives a quotation, they expect the information to be presented in a way they are accustomed to reviewing within their sector. A lack of standardization introduces ambiguity, skepticism, and delays. For example, specific jargon, units of measure (e.g., man-hours vs. square footage), and liability clauses must be present and correctly contextualized to prevent misunderstandings.

Furthermore, many industries, especially those heavily regulated or reliant on public tenders, require compliance with national or international standards. Incorrect formatting or missing statutory details can invalidate a bid, regardless of how competitive your pricing may be. Standardized formats act as an internal quality control mechanism, ensuring all necessary data points—from tax identification numbers to warranty periods—are included.

Format Variations Across Key Industries

The core components of a quote might seem universal (cost, scope, timeline), but their presentation and necessary appendices vary wildly:

The Construction Sector’s Need for Detail

Construction quotes are renowned for their complexity. They require granular breakdown structures, often utilizing standardized numbering systems (like CSI MasterFormat). A construction quote must clearly delineate between materials costs, labor costs, overheads, permits, and provisional sums. Crucially, they must explicitly define exclusions and conditions related to site access, weather delays, and variations (change orders). Without these specifics, both the contractor and the client are exposed to significant financial risk.

IT and Software Development: Scope and Deliverables

IT quotations focus heavily on defining the scope of work (SOW) and deliverables, often struggling with intangible elements. Instead of material lists, IT quotes emphasize licensing fees, maintenance agreements (SLA details), and intellectual property ownership. The format often relies on tiered pricing models (fixed price, time and materials, or subscription) and must clearly articulate acceptance criteria for project completion, protecting both parties from “scope creep.”

Professional Services: Transparency in Pricing

In fields like consulting, legal, or accounting, the value lies in expertise. Quotations here must prioritize transparency regarding hourly rates, the seniority of staff allocated, and itemized administrative fees. Unlike product-based industries, the format should clearly explain how estimated effort translates into projected cost, often utilizing phased breakdowns to offer clients flexibility and predictable budgeting.

Leveraging Technology for Optimal Formatting

Manually generating complex, industry-specific quotes is error-prone. Modern businesses are turning to dedicated quotation software (CPQ systems) that automate the inclusion of necessary compliance data, legal templates, and industry-specific pricing variables. These tools ensure every quote generated adheres strictly to the required format, enhancing efficiency and dramatically improving the firm’s conversion rates.

Ultimately, a successful quotation is more than just a price tag—it is a formal business communication that reflects meticulous planning and deep industry understanding. By mastering the required format for your sector, you build client trust, mitigate legal risk, and establish a robust foundation for long-term profitability.

Tagged : / / / / / / /

Storing Payment Receipts Securely: Essential Best Practices for Business Compliance and Audit Readiness

Why Secure Receipt Storage is Non-Negotiable

Payment receipts are more than just transaction records; they are critical financial documents containing sensitive data, often including customer details, purchase history, and sometimes partial payment card information. For businesses, securely storing these receipts is not merely a logistical challenge—it is a legal mandate essential for tax compliance, financial auditing, dispute resolution, and safeguarding customer privacy.

Failure to implement robust storage protocols can expose businesses to severe fines, data breaches, and reputational damage. Adopting best practices ensures compliance with critical regulations like PCI DSS (if handling card data) and general data protection laws (like GDPR or CCPA).

Understanding Legal Obligations and Retention Periods

One of the primary steps in secure receipt management is knowing how long you must keep them. Retention requirements vary significantly based on jurisdiction and the type of document. In the US, the IRS generally requires businesses to keep records supporting tax filings for three to seven years, depending on the circumstances. Businesses must establish a clear retention policy that meets the strictest applicable legal standard.

Crucially, once the retention period expires, secure disposal is mandatory. Simply throwing away sensitive receipts creates a vulnerability. For physical records, cross-shredding is required; for digital files, certified data sanitization is necessary.

The Shift to Secure Digital Receipt Storage

Modern businesses overwhelmingly prefer digital storage due to its efficiency, searchability, and reduced physical footprint. However, digitizing receipts introduces new security risks that must be managed. Digital files are susceptible to hacking, system failure, and unauthorized access.

Key Digital Best Practices:

  • Encryption: All stored receipt files must be encrypted both in transit (when uploading) and at rest (on the server or cloud). Use strong, industry-standard encryption protocols (e.g., AES-256).
  • Secure Backups: Implement geographically diverse, redundant backups to protect against data loss from natural disaster or system failure.
  • Access Control: Utilize the principle of least privilege. Only authorized personnel should have access to the directories containing receipt data. Use multi-factor authentication (MFA) for accessing storage systems.

Handling Physical Receipts and Destruction

Even in a digital world, some physical receipts persist. These documents require immediate and secure handling to prevent ‘shoulder surfing’ or simple theft. Physical storage facilities must be locked, access-controlled, and monitored.

The most critical step for physical records is destruction. Never rely on standard trash disposal. Invest in high-security cross-cut shredders that meet government standards, or partner with a certified document destruction service that provides a certificate of destruction.

Implementing a Comprehensive Receipt Security Policy

A successful secure receipt storage strategy relies on a formalized, documented policy that all employees understand and adhere to. This policy should cover the entire lifecycle of a receipt, from point of transaction to final destruction.

Regular security audits are essential to identify weak points in the storage infrastructure. Compliance checks, especially regarding PCI DSS requirements for masking sensitive payment card information (known as truncation), should be routine. Training staff on phishing awareness and proper handling of sensitive data is the final, crucial layer of defense in maintaining the security and integrity of stored payment receipts.

Tagged : / / / / / / /

Securely Storing Payment Receipts: Essential Best Practices for Business Compliance and Data Protection

Why Secure Receipt Storage is Non-Negotiable

For businesses of all sizes, payment receipts are more than just proof of transaction; they are critical documents containing sensitive financial and customer data. Neglecting proper storage protocols exposes your business to severe risks, including massive fines under regulations like PCI DSS (Payment Card Industry Data Security Standard), data breaches, and significant loss of customer trust. Implementing a comprehensive strategy for securely storing payment receipts is not optional—it is a mandatory pillar of modern business compliance and data protection.

Understanding Legal and Compliance Requirements

The first step in securing payment data is understanding your legal obligations. PCI DSS mandates strict rules regarding the handling of cardholder data. Crucially, businesses should never store the full Primary Account Number (PAN), card verification values (CVV), or the PIN. Receipts, both digital and physical, must mask or truncate card numbers effectively. Beyond financial regulation, tax authorities often require businesses to retain receipts for audit purposes, typically ranging from three to seven years, depending on jurisdiction. Your storage system must therefore balance security with efficient retrieval for auditing.

Best Practices for Digital Receipt Storage

The majority of modern businesses utilize digital record-keeping, which offers efficiency but requires robust cybersecurity measures. To securely store digital receipts:

  • **Encryption is Key:** All stored receipt files must be protected using strong, industry-standard encryption (such as AES-256), both while at rest (on servers) and in transit (when accessed).
  • **Implement Access Controls:** Utilize the principle of least privilege. Only employees who absolutely require access to receipt data for their roles (e.g., accounting) should be granted permission. Access should be monitored via audit logs.
  • **Utilize Secure Cloud Services:** If using cloud storage, ensure the provider is compliant with relevant security standards (e.g., ISO 27001) and offers advanced features like Multi-Factor Authentication (MFA) and geo-redundancy for disaster recovery.
  • **Regular Backups:** Encrypted backups should be performed regularly and tested to ensure data can be recovered quickly in case of system failure or ransomware attack.

Managing and Destroying Physical Receipts

While digital storage dominates, physical paper receipts still exist and pose unique security challenges. They must be treated with the same level of security as digital files. Store paper receipts in locked, fireproof filing cabinets accessible only to authorized personnel. When the required retention period expires, secure destruction is paramount. Do not simply throw them away; use a cross-cut shredder that meets security standards, or hire a certified document destruction service.

Establishing Clear Retention and Destruction Policies

A formalized retention policy is essential. This policy must clearly define:

  1. How long each type of receipt must be kept, based on regulatory minimums.
  2. The secure procedure for data destruction (e.g., automated deletion for digital files; certified shredding for physical copies).
  3. The required documentation proving that destruction occurred securely and completely.

By proactively implementing these detailed best practices, businesses can move beyond mere compliance, enhancing operational security and safeguarding their reputation against the ever-present threat of data compromise.

Tagged : / / / / / /

Storing Payment Receipts Securely: Essential Best Practices for Business Data Protection

The Criticality of Secure Receipt Management

For any business handling transactions, payment receipts are more than just proof of purchase—they are vital documents containing sensitive data, including parts of card numbers (PANs), dates, and customer details. Failing to implement robust secure payment receipt storage protocols exposes businesses to severe risks: financial fraud, costly compliance penalties (such as PCI DSS violations), and irreparable damage to customer trust. Ensuring secure, compliant storage is not optional; it is a fundamental pillar of modern business operations.

Digitalization: A Double-Edged Sword in Receipt Handling

While moving away from piles of physical paper receipts reduces physical clutter, digitalization introduces new complexities. Physical receipts must be stored in locked, fireproof environments with restricted access. However, the majority of businesses now rely on digital records. Digital receipts offer efficiency, but they require a sophisticated approach to data security. Businesses must avoid storing raw card data entirely, adhering strictly to PCI DSS standards that dictate what sensitive authentication data can and cannot be retained.

Implementing Robust Digital Storage Protocols

The foundation of effective digital receipt security lies in controlling access and encrypting data both in transit and at rest. Best practices demand using strong, industry-standard encryption algorithms (like AES-256) for all archived receipts. Access should be governed by the principle of least privilege (PoLP); only authorized personnel who explicitly require access for audits or customer service should be able to retrieve stored data. Furthermore, businesses should utilize dedicated, secure cloud solutions or internal servers that feature multi-factor authentication (MFA) and continuous monitoring for suspicious activity. Regular vulnerability assessments are crucial to identifying and patching potential weaknesses in the storage environment.

Compliance, Retention, and Data Minimization

A defined receipt retention policy is essential. Regulatory bodies and tax authorities often mandate that records be kept for a specific period (typically 3 to 7 years). Once this mandatory period expires, the data must be securely and irrevocably destroyed, a process known as data minimization. Keeping data longer than necessary increases liability. When designing your secure payment receipt storage strategy, prioritize systems that automate deletion processes and provide comprehensive audit trails detailing when, how, and by whom data was accessed or destroyed. This meticulous record-keeping is vital for demonstrating due diligence during compliance audits.

Choosing the Right Tools for Security

To fully secure payment receipts, invest in tools that specialize in document management and archival with built-in security features. Look for solutions that offer tamper-proof logging, geo-redundancy (backing up data in multiple locations), and high-level certifications like ISO 27001. By adopting these best practices for businesses, companies can transform their receipt storage from a compliance headache into a strategic asset that safeguards both customer information and the bottom line.

Tagged : / / / / / /

Storing Payment Receipts Securely: Best Practices for Businesses in the Digital Age

The Criticality of Secure Receipt Storage

For businesses of all sizes, payment receipts are more than just transaction records; they are vital documentation for accounting, auditing, and regulatory compliance. However, these documents often contain sensitive data, including partial card numbers, customer names, and transaction specifics. Storing payment receipts securely is not optional—it is a mandatory pillar of data protection and operational integrity.

Failure to implement robust security measures can lead to severe financial penalties, regulatory fines (such as those related to PCI DSS or GDPR), and devastating reputational damage. Adopting best practices ensures your business remains compliant and resilient against data breaches.

Regulatory Compliance and Retention Periods

One of the primary drivers for secure storage is regulatory compliance. Different jurisdictions and industries impose varying retention periods for financial records. For instance, IRS requirements typically mandate holding receipts for several years, while specific payment card industry (PCI) standards dictate how sensitive payment data must be handled or immediately destroyed.

Businesses must clearly define retention schedules based on legal advice. Crucially, once a receipt has met its required retention period, it must be disposed of using secure methods—shredding for physical copies and permanent digital deletion or cryptographic destruction for electronic files.

Digitalization: The Modern, Secure Solution

While physical filing cabinets were once standard, modern businesses are transitioning to digital receipt storage systems. Digitalization offers superior security, searchability, and scalability.

When migrating to digital storage, key practices include:

  • Encryption: All stored data (data at rest) must be encrypted using strong, industry-standard algorithms (e.g., AES-256).
  • Access Controls: Implement the principle of least privilege. Only authorized personnel should have access to the receipt archive, enforced through strong passwords and multi-factor authentication (MFA).
  • Cloud Security: If utilizing cloud services, ensure the provider is compliant with relevant security standards (like SOC 2 or ISO 27001) and understand their shared responsibility model regarding data protection.

Essential Physical and Digital Security Measures

Even in a digital world, some businesses still handle paper receipts. Secure physical storage involves locking file rooms, limiting access, and monitoring the storage environment.

For both physical and digital systems, continuous vigilance is key:

  • Tokenization and Masking: Never store full card numbers (PANs). If sensitive data must be retained, ensure it is masked or replaced with non-sensitive tokens immediately after transaction processing.
  • Regular Audits: Conduct periodic internal audits of storage logs and access permissions to identify and remedy potential vulnerabilities.
  • Backup Strategy: Implement redundant backups (e.g., 3-2-1 rule) that are themselves securely encrypted and stored offsite, guaranteeing business continuity in case of system failure or disaster.

By integrating these secure practices, businesses not only safeguard customer trust but also establish a robust foundation for long-term operational success and compliance.

Tagged : / / / / / /